The UK’s top financial watchdogs have ordered banks to be prepared to rebuild their systems from scratch if hit by a cyberattack following an explosive rise in new threats.
The Bank of England and Financial Conduct Authority (FCA) have introduced a new set of guidance that brings responsibilities for firms in line with the National Cyber Security Centre’s Cyber Assessment Framework.
Under the new guidance, which is open for consultation until late February, firms must operate on the assumption that a major cyberattack will breach their defence.
Companies will be required to maintain response and recovery playbooks that include rebuilding core banking systems completely from scratch, without relying on potentially tainted backups.
“Where proportionate, response and recovery testing should move beyond traditional tabletop exercises and assess areas, such as how quickly a firm could complete a bare metal rebuild,” the consultation paper said.
Stay in the know
Three daily briefings with the key market moves and top business and political stories.
SUBSCRIBE HEREFinancial services firms will be supervised against the guidance and there will be enforcement powers for the regulators.
The consultation paper also puts banks on the hook, even when outsourced tech fails. It expects firms to map vulnerabilities across its supply chain, which includes open source software and physical infrastructure.
Cyber incidents reach second-highest month in five years
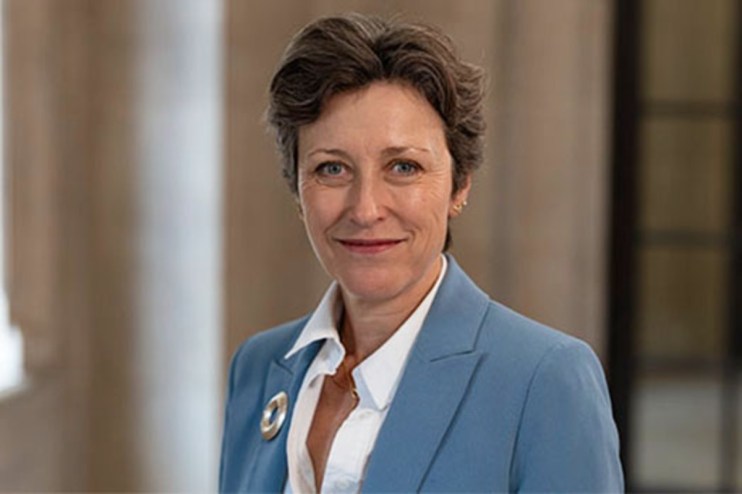
“Firms must increase attention to their operational and cyber resilience, and critically to their core cyber hygiene practices which remain the most significant mitigant to current risks,” Katharine Braddick, chief executive of the Prudential Regulation Authority, told an audience of industry leaders on Wednesday.
“And we will give these issues a materially greater weight in our supervision.”
Braddick said the financial system was entering a “risk environment that generates a new and startling news story every few days, and many more incidents that do not reach the public sphere”.
The banking watchdog boss said the first meeting of a new Systemic Resilience Council will be held in the coming weeks, which will bring together authorities and the bosses of systemically important firms to identify shared vulnerabilities.
The FCA said it saw the second-highest monthly number of reported cyber incidents in five years in October, 52 per cent above the previous 18-month peak in May 2025.
The consultation paper warns AI capabilities are doubling every eight months, allowing attackers to exploit vulnerabilities in mere hours as opposed to weeks or months.
It tells firms to shift from “vulnerability management” to continuous “exposure management”.
The watchdogs estimate the proposals will cost the sector £7m a year, which would break even if it prevents 3.5 per cent of UK financial data breaches.
A survey from the Bank of England and FCA found 88 per cent of respondents expect frontier AI cyber capabilities to have a moderate or high impact on their risk profile over the next two years.
“Technology moves fast, and so do cyber threats,” Nikhil Rathi, chief executive of the FCA, said.
“Firms have asked us for clarity about what good cyber resilience looks like. This guidance provides it, helping strengthen their resilience, protect clients and the services they rely on.”